The 2026 renewal market quietly turned your insurance application into a security audit. The companies that read the memo will pay less and sleep better. The ones treating it as paperwork are writing checks they will never get back.
The polite fiction is over
Cyber insurance requirements 2026 didn’t arrive with much warning. There was a comfortable stretch, roughly 2024 into 2025, when cyber insurance felt like it was getting cheaper and easier. Average premiums actually fell about 11 percent in 2025, according to Lockton. Underwriters competed on price. You filled out a form, checked a few boxes, and a policy showed up. It was pleasant. It was also a setup.
Because while everyone enjoyed the discount, the claims went the other direction. The NAIC counted roughly 50,000 cyber claims, a 40 percent jump year over year (StationX, 2026 statistics). Coalition, which insures more than 100,000 organizations, found initial ransom demands surged 47 percent, even as most businesses refused to pay (Coalition 2026 Cyber Claims Report). The math there is not subtle. When you take in less and pay out more, you do not stay solvent by being generous. You stay solvent by getting selective.
The reversal, with numbers
S&P Global Ratings now expects cyber premiums to climb 15 to 20 percent in 2026, and it is not shy about why: rising claim severity, more data theft, and the new variable of AI-driven attacks. The same research projects the market reaches roughly 23 billion dollars in premium by 2026, up from about 14 billion in 2023 (Insurance Business, Industrial Cyber). That is not a market softening. That is a market that found its spine.
And here is the part nobody puts in the renewal email: the price is the least interesting thing that changed.
Your application is now a technical audit
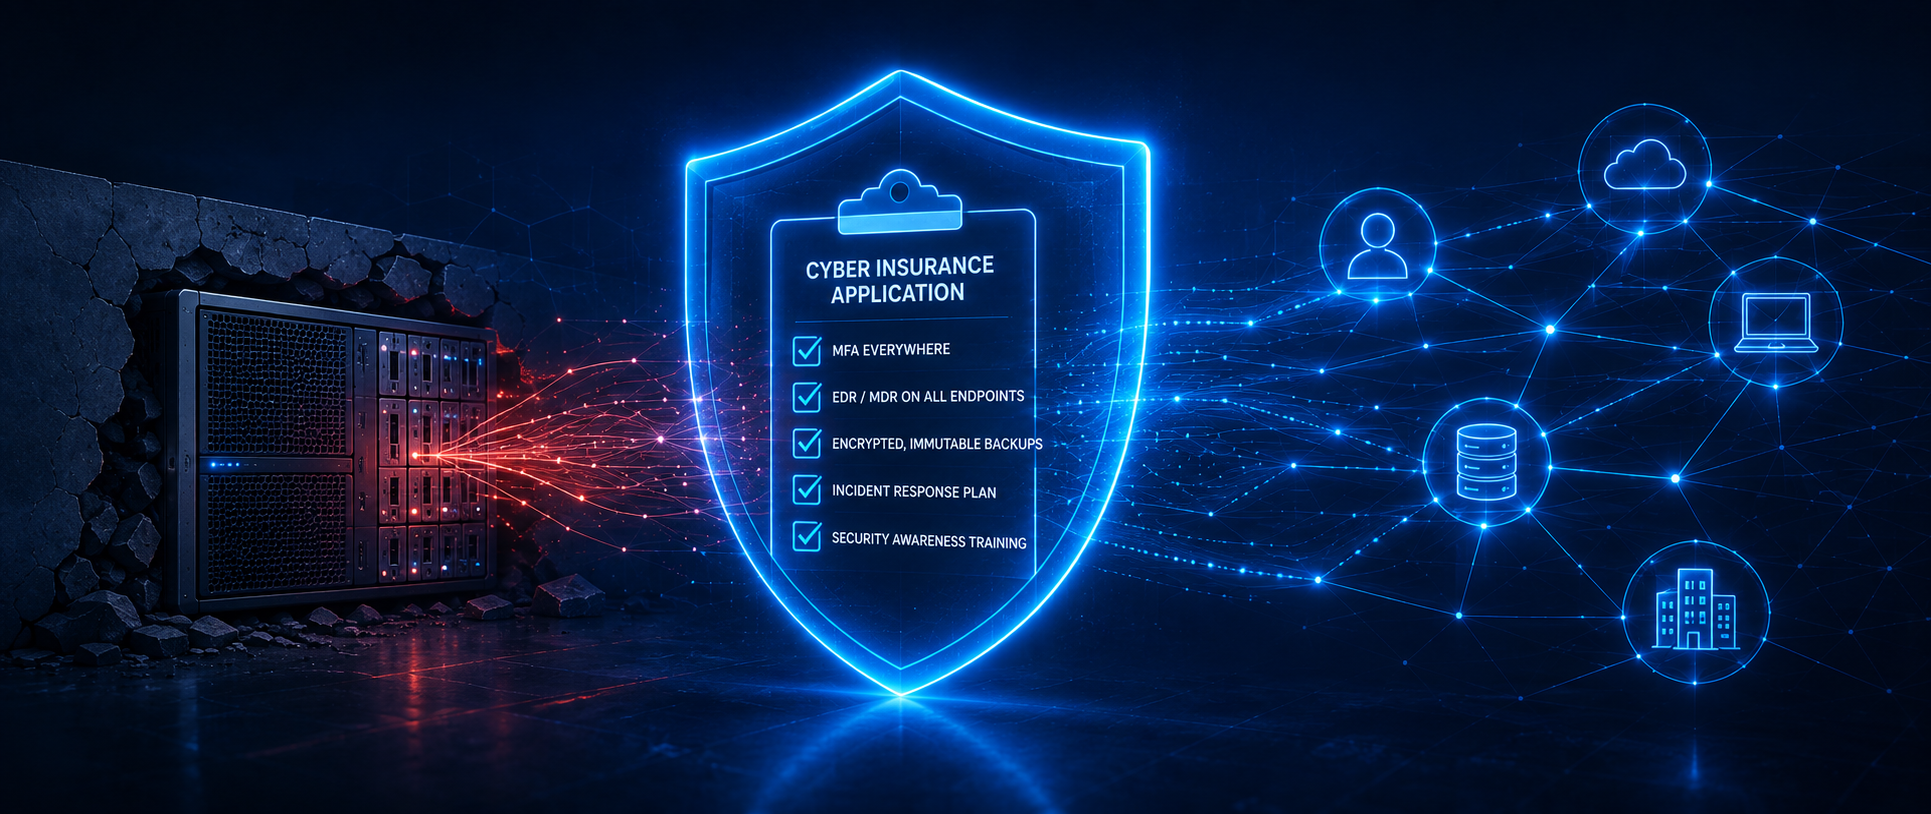
Somewhere along the way the cyber insurance application stopped being a questionnaire and became an exam with a proctor. The 2026 requirement set reads like a security framework because it is one: MFA on every access path, EDR or MDR on every endpoint including servers, encrypted and immutable backups that you have actually tested, a written incident response plan, and security awareness training (Consilien 2026 readiness checklist). Aon’s 2026 cyber market report confirms that underwriting now turns on control maturity, vendor dependencies, and how you use AI (Todyl analysis).
Translated: your insurer has opinions about your architecture, and it is grading you.
For most mid-market companies, meeting that bar means running detection and response around the clock. You either stand up a security operations center, which you will not, or you contract MDR with real response SLAs, which you should. The insurer is no longer suggesting managed security. It is a condition of the policy.
What happens if the application isn’t quite true
Meeting the requirements on the application is not the same as being covered. You also have to have been telling the truth. Continuously.
Ask International Control Services. In a 2022 case that still holds up as the clearest example on record, Travelers issued ICS a cyber policy, ICS got breached, and Travelers found the attack began on a server that did not have the MFA the application claimed was in place. ICS ultimately agreed to a consent judgment rescinding the policy (Triton Technologies on Travelers v. ICS, MFA claim-denial breakdown). The policy did not pay. The premiums did not come back. The company had insurance right up until the exact moment it needed it, at which point it had a voided contract.
The legal standard makes this worse, not better. Across most US jurisdictions, an insurer can rescind a policy for a material misrepresentation on the application whether the misstatement was intentional, negligent, or an honest mistake. Intent is not required, and the gap does not even have to be what caused the breach. You said you had the control, you did not have it everywhere, the policy is void.
So the modern cyber policy has two ways to fail you. You can fail to qualify, or you can qualify by attesting to a control you cannot actually back up, then discover at claim time that the policy is worthless exactly when you need it.
Why the mid-market is the soft target
Coalition’s data shows large companies get hit more often, about five times more than smaller ones. That reads like good news for the mid-market until you remember why. Big enterprises have staff, tooling, and a SOC. The 200-to-2,000-employee company with a two-person IT team carries the same attack surface and almost none of the standing defense. You are not too small to be a target. You are the right size to be an easy one, and now your insurer knows it too.
Add a regulated vertical, healthcare, finance, or manufacturing with OT, and the stakes compound. HIPAA and PCI already demand controls. The carrier wants proof of the same controls. A breach then triggers a regulatory investigation and a coverage fight at the same time. That is not a scenario you want to meet for the first time during an incident.
The case for getting ahead of it
Here is the strategic read, and it is boring in the best possible way. The controls the insurer is demanding are the same controls that keep you from filing a claim in the first place.
MFA everywhere. Monitored endpoints. Tested backups. A rehearsed incident response plan. That is not an insurance tax. That is competent security with a financial incentive stapled to it. Get ahead of it and you win three ways. You qualify for coverage. You negotiate from strength instead of scrambling against a renewal deadline. And you become materially harder to breach, which was the entire point before insurance ever entered the conversation.
Wait, and you get the mirror image. You renew under pressure, accept whatever terms are on the table, attest to controls you have not verified, and learn the truth about your coverage on the worst day of your company’s year.
Getting ahead of it costs less than the premium increase. It costs far less than the denied claim.
Before You Renew
Get a Cyber Insurance Reality Check
Have a renewal notice sitting in your inbox? Bring it if you like, it helps, but it’s not required. We map what your policy actually requires against what you can verify today, then show you exactly what needs to close before the next renewal, not after a claim gets denied.
—
Your policy’s actual requirements, checked against your real environment.
—
A gap list you can act on, not a generic security score.
—
No pricing pitch. A straight read before your renewal lands.
No obligation. Bring your renewal notice if you have one, or come with questions.
Where Matrix fits
This is the work we do for lean IT teams that cannot stand up a 24 by 7 security operation on their own. We map your environment to what carriers actually require, close the gaps that get claims denied, and run the managed detection and response that turns an insurance checkbox into a documented, continuously maintained reality. The goal is not to pass the application. The goal is to make the application true, and keep it true.
Your insurer already decided it is your CISO. You can let it run your security program by remote control through a renewal form, or you can own the program, meet the bar on your terms, and treat the policy as the backstop it was always meant to be.
The renewal is coming either way. Read the fine print before it reads you.
Not sure where your gaps are? Request a cyber insurance readiness assessment from Matrix Networks. We’ll map your current controls against what carriers are asking for and show you exactly what needs to close before your next renewal, not after a claim gets denied.